


Rudy Systems / Selected work / All repositories
I'm Raven, founder of Rudy Systems. I build tools for systems programming, network reconnaissance, and security research, with a focus on evidence you can inspect.
My main focus is Rudy Evidence, a shared security SDK with a C++20 core, a C ABI, and C# and Python bindings. I also build endpoint research tools, a Linux security workbench, and focused tools for HTTP/TLS, DNS, and public-source intelligence.
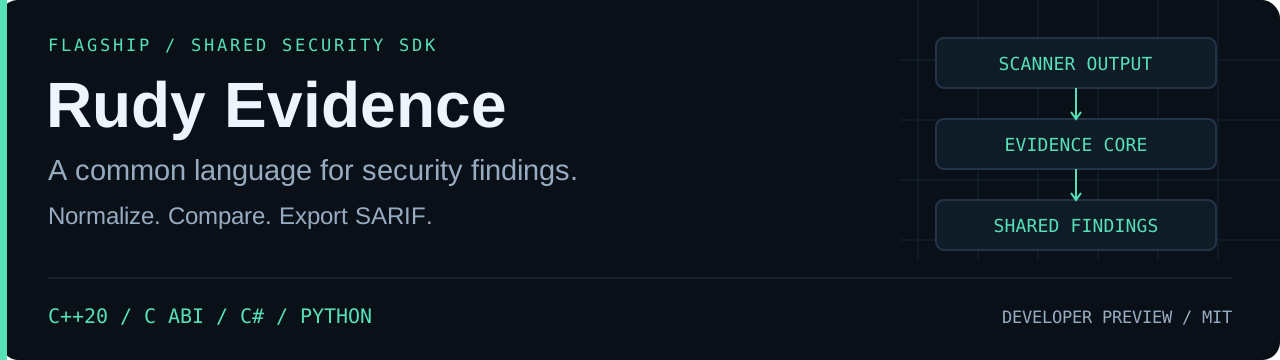
Rudy Evidence is the shared foundation for my security tools: a native SDK that normalizes scanner findings, redacts recognized secret patterns, merges exact duplicates, compares baselines, and exports SARIF.
C++20 · C ABI · C# · Python — seven report adapters, offline processing, and integrations in Web Audit, Sentinel, and Central. v0.1.0 / developer preview; MIT licensed.
Explore the SDK · Download the preview · Build and test status
Process activity, behavioral correlation, and a Windows investigation console. Research preview: unsigned driver; kernel runtime validation pending. |
Authorized assessment, bounded Linux kernel telemetry, and signed evidence in one browser workspace. Early platform: v0.2.0; source private. |
| Tool | What it does |
|---|---|
| Web Audit | HTTP/TLS checks, redirect tracing, baseline comparison, SARIF and native evidence export |
| RudyNET | TCP/UDP checks, service banners, HTTP/TLS inspection, and DNS discovery |
| DNS Checker | DNS records, WHOIS lookups, and SPF/DMARC policy summaries through Discord |
| IP Checker | Shodan, VirusTotal, WHOIS, and Tor exit-node observations through Discord |
| Username OSINT | Public username discovery through Sherlock, with candidate profile links in Discord |
| Breach Checker | Breach-source lookups through Discord using a configured, compatible provider |
| Metadata Checker | Image EXIF and PDF document-information inspection through Discord |
- Closer to the system: native components, documented OS interfaces, and bounded event processing.
- Shared foundations: reusable libraries, stable contracts, and evidence that moves between tools.
- Clearer investigations: traceable observations, replayable evidence, and useful exports.
- Tools that hold up: reproducible builds, meaningful checks, and explicit validation status.
RUDY SYSTEMS
rudy.systems ·
LinkedIn